We pair automated and manual discovery with expert review, and exploit high-impact issues by hand, so your report shows real risk, not scanner noise.
Four stages. The right intelligence at each step.
Identify attack surface, exposed functionality, assets and potential security weaknesses.
Investigate findings, correlate evidence and determine what actually matters.
Manually verify security findings and distinguish real risk from false positives.
Turn validated findings into clear, actionable security assessment reports.
Security expertise that helps you find and close critical gaps.
Test AI applications for real-world vulnerabilities, including prompt injection, data leakage and RAG risks.
Identify misconfigurations, excessive privileges, exposed services and realistic cloud attack paths.
Deep security testing for web applications and APIs, including authentication, authorization and business logic.
We help your team understand the findings, prioritize the risks, and address the security gaps.
Sample Assessment Reports. Clear Security Insights.
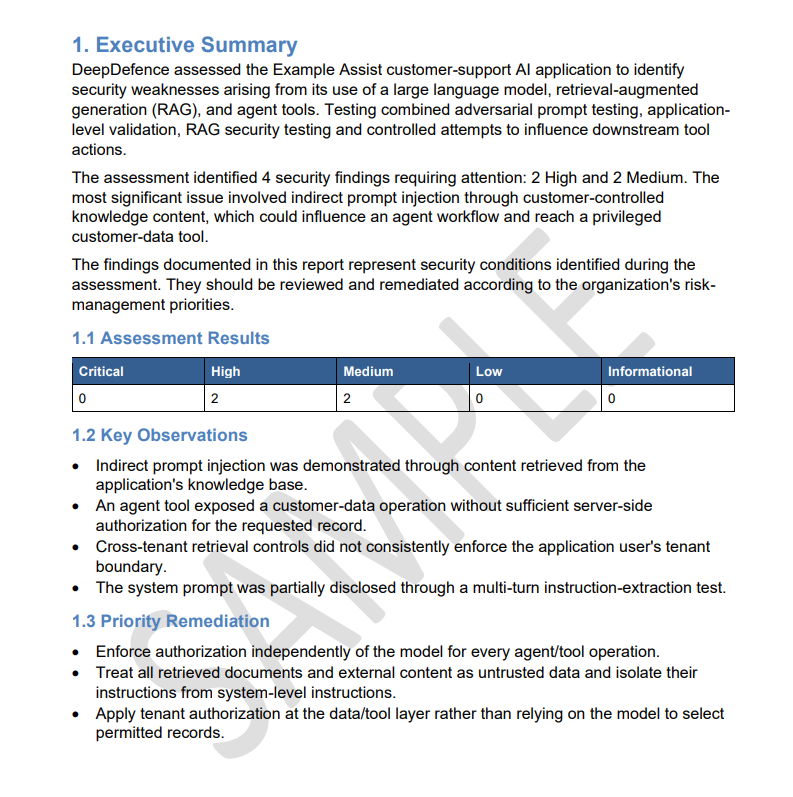
Sample assessment showing AI application security findings.
View Sample Report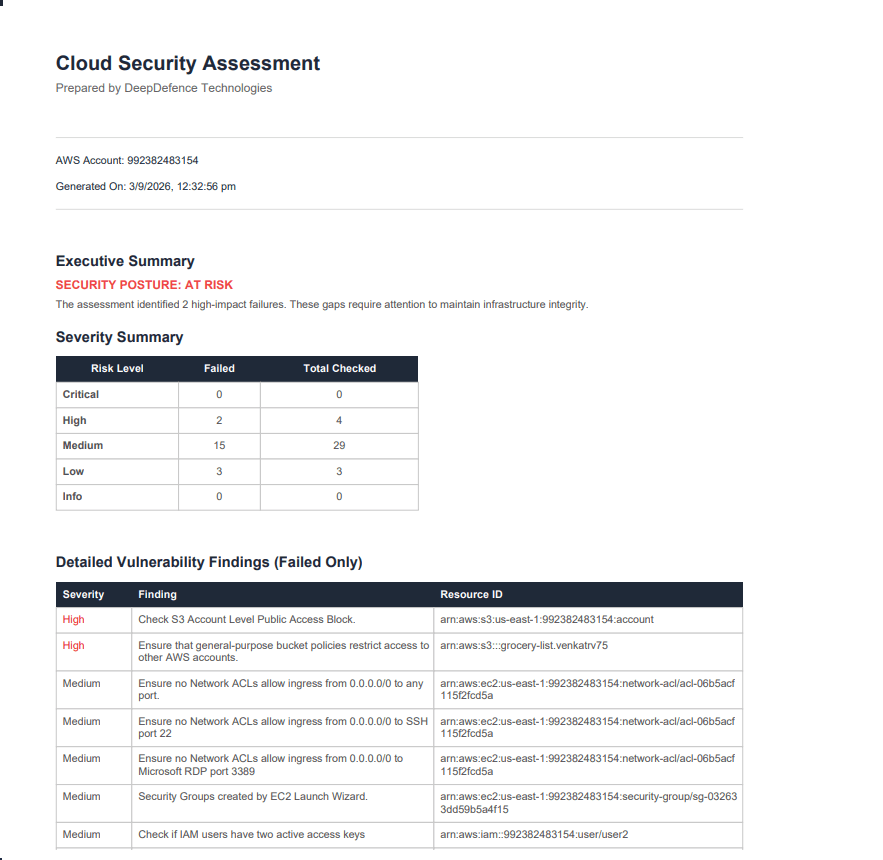
Sample AWS security assessment covering cloud configuration, exposure and security findings.
View Sample Report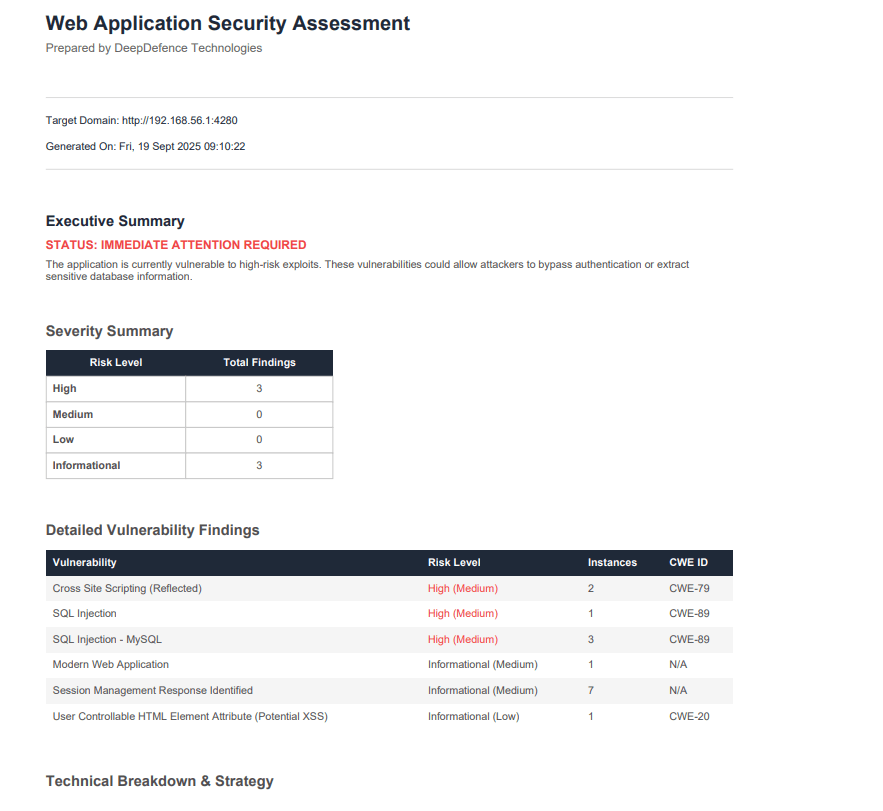
Sample assessment showing vulnerability findings, severity, evidence and technical details.
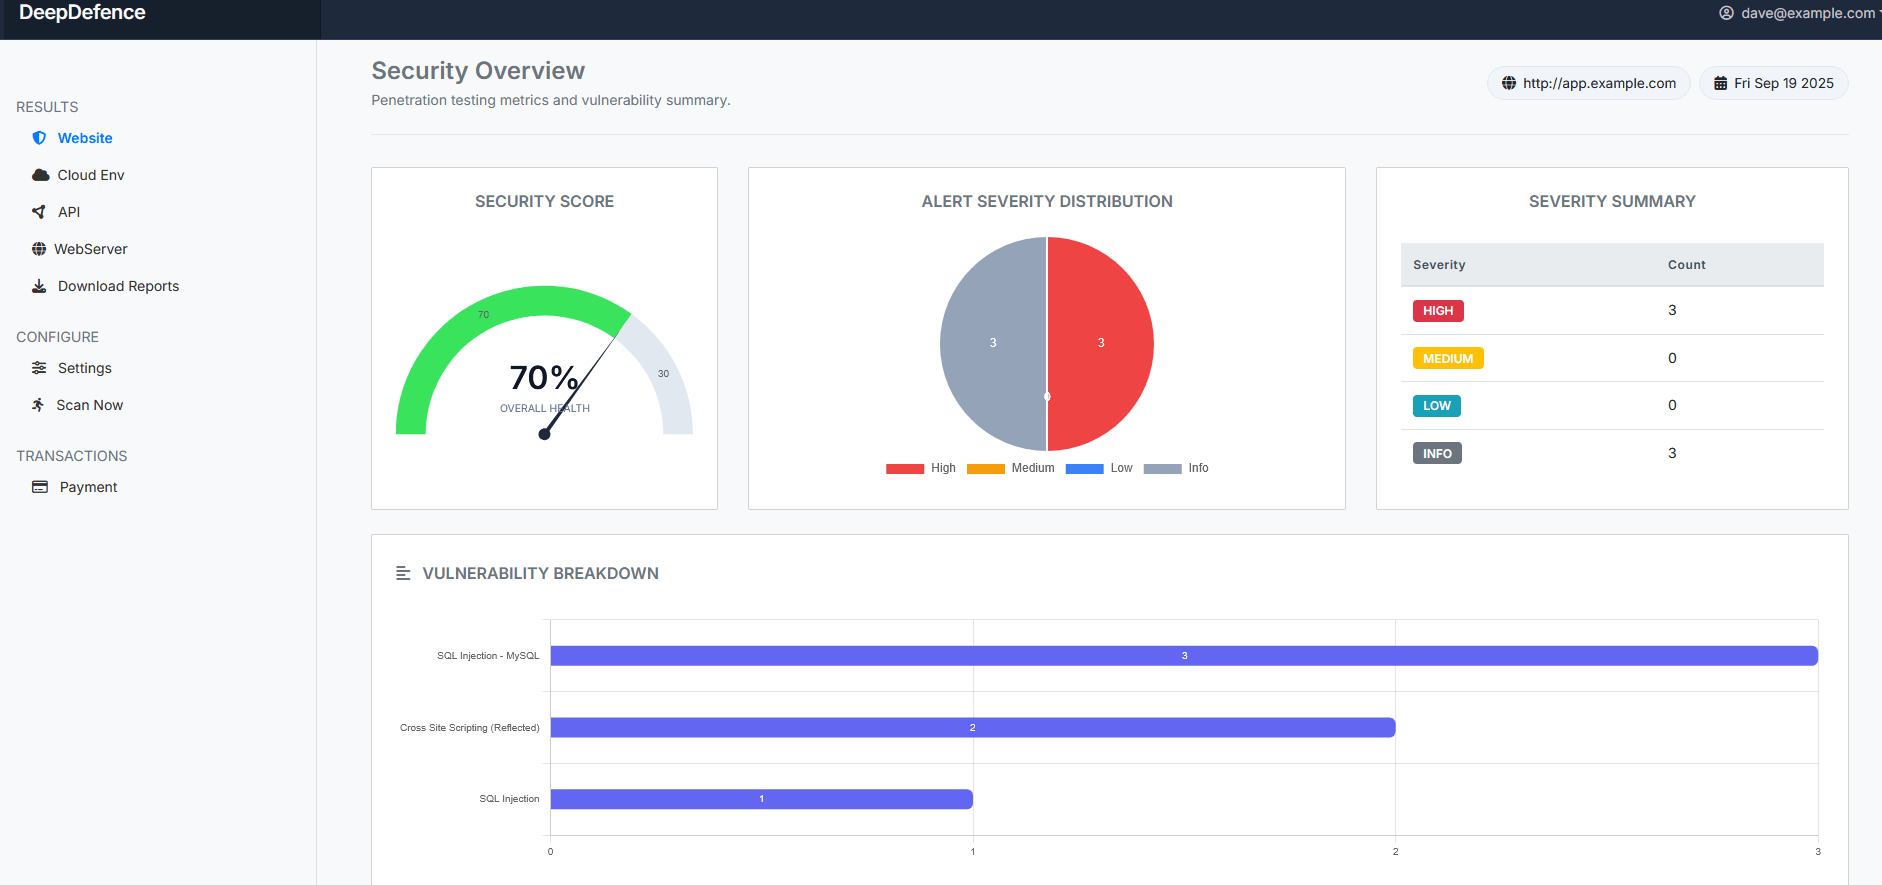
View Sample ReportIn addition to the detailed assessment report, DeepDefence clients get access to our online assessment platform to review their security posture, findings and assessment results through interactive dashboards.
Client access is provided with your DeepDefence assessment.
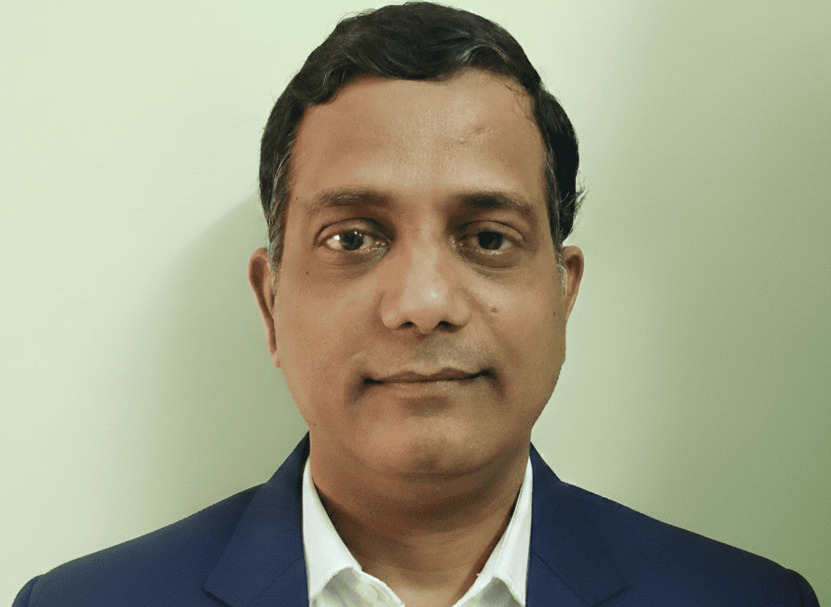
DeepDefence is founded and led by a cybersecurity professional with 25+ years of IT experience, specializing in AI security, AWS/cloud security, application security, and penetration testing.
Our approach combines automated and manual discovery, AI-assisted analysis and human-led exploitation to identify vulnerabilities that automated tools alone can miss.
Teams rely on DeepDefence to secure production systems, meet regulatory requirements and ship with confidence.
 HIPAA · Healthcare on AWS
DeepDefence secured our HIPAA healthcare application on AWS. The cloud and application controls they implemented helped us expand the platform, and their periodic penetration testing kept us aligned with regulatory requirements. They also worked directly with our clients on security integration.

Subdomains, exposed services, email & DNS security, TLS certificates, lookalike domains, and an overall exposure score.
Discovering externally visible information for .
This usually takes two to three minutes.
Everything you need to know before getting started
Drop a few details below. We'll help you define the scope and provide a clear, fixed quote — or we can hop on a quick call if your requirements are complex.
Prefer direct communication? Reach out and we’ll get back within 24 hours.
info@deepdefence.co
Phone
+91 83176 55901
Location
Hyderabad, India
We primarily work with remote clients across India and globally.


